GETEC has achieved a major milestone on its path toward harmonising information security across Europe, with the successful ISO 27001 certification in Germany and Italy.
For any company’s information security management systems, the risk of cybercrime is a serious concern, due to phishing, ransomware and other data breaches. With digital technologies constantly evolving, new threats continue to emerge. Companies need to be risk-aware and to regularly identify and address weaknesses.
The ISO 27001 is the leading global standard for information security. It protects data confidentiality, establishes the infrastructure to mitigate risks and ensures compliance across a range of IT systems. GETEC has received this certification in Germany and Italy. It shows we are strengthening our European security strategy while also enhancing risk management, cyber-resilience and operational excellence. Our holistic approach covers the vetting of people and policies, improving security controls and aligning with current security standards.
“As we continue to harmonise our information security across Europe, this certification confirms the effectiveness of our company-wide efforts,” says Gunar Korm, Chief Information Security Officer at GETEC. “It also reinforces our strategic commitment to trust, stability, top-tier security and high-quality standards.”
In Europe, an estimated 1-in-5 EU enterprises experienced security incidents in 2023, with the electricity, gas and water supply sectors heavily targeted. A rising concern is Distributed Denial of Service (DDoS) attacks that attempt to overload the targeted system, causing unplanned shutdowns and damage to organisations or companies that can have serious knock-on effects.
At GETEC, we view energy supply and information security as inseparable components of a stable and resilient future.
Chief Information Security Officer
Securing our digital future
GETEC has a clear strategic approach to cybersecurity: it is a cornerstone of our corporate governance, as we continue to unify our information security management systems and make resilience a guiding entrepreneurial principle.
“Cybersecurity is no longer a cost factor, but a business enabler for growth, supported by reliable and certified processes,” says Marco Appendino, IT Infrastructure & Security Manager at GETEC. “Security translates directly into trust and market opportunities, for existing customers as well as for new business.”
The ISO 27001 is the leading global standard for information security.
The successful ISO 27001 audits in Germany and Italy prove that GETEC has a high level of security architecture in place. We are planning further rollout across the European countries where we work, to establish a unified security culture and achieve the certification in our European subsidiaries. As the ISO 27001 is a crucial proof of trust for customers and partners, it results in information security being a key competitive differentiator and a driver of growth in the energy sector.
What is ISO 27001?
It is the world’s best-known standard for information security management systems, defining the requirements these systems must meet. It provides companies with guidance for establishing, implementing, maintaining and continually improving cybersecurity. Receiving the certification means the company has systems that manage risks related to the security of data owned or handled by the company, aligned with the best practices and principles of the international standard.
Highlights
-
Building a brand that delivers on its promises
Read more -
Rethinking resilience – a new understanding of sustainability in the energy sector
Read more -
New HSEQ dashboard supports decision-making, performance and safety
Read more -
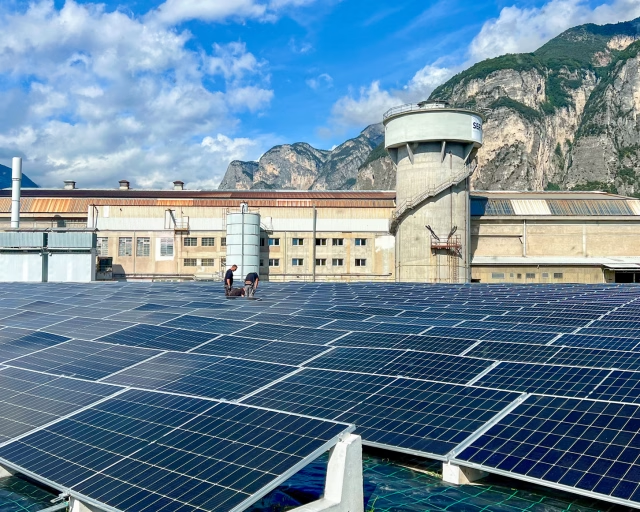
Solar panel system reduces emissions at production plant in Italy
Read more -
New motor reduces energy consumption at Muttenz industrial park
Read more -
Decarbonisation for the SMS group
Read more -
Flexible solution improves energy efficiency at commercial site in Berlin
Read more
